BOTNETSECURITY
Services ⌄
PEN TESTINGWeb applicationAPI securityMobile applicationCloud securityNetwork + infrastructureSAP
AI SECURITYAI + LLMMCP securityView all services →
OFFENSIVE SECURITYRed Team assessmentPurple Team engagementSocial engineeringControl / evasion validationInsider simulation
Red Team
BotXpose ⌄
PLATFORMProduct overviewAutonomous AI pentestingHow it worksTesting coverage
TRUST + DELIVERYProof & evidenceAuthorization & safetyIntegrations & workflow
PartnersBlogCompanyContact
Request Assessment ↗
Menu
PEN TESTINGServices overviewWeb applicationAPI securityMobile applicationCloud securityNetwork + infrastructureSAP penetration testingAI + LLMMCP security OFFENSIVE SECURITYRed Team overviewRed Team assessmentPurple TeamSocial engineeringControl validationInsider simulation PRODUCTBotXpose overviewAutonomous AI pentestingHow it worksProof & evidenceAuthorization & safetyTesting coverageIntegrations & workflow COMPANYBlogPartnersCompanyContact Request Assessment
  1. Home
  2. Blog
THE BOTNET SECURITY BLOG

Research & insights

Practical security research. Real assessment lessons. Clear takeaways.

Latest articles6 articles
Beyond the Login: a signed-in identity meets an independent authorization gate before protected records.
Web Application SecurityLatest

Beyond the Login

A visual guide to identity, authorization and tenant boundaries.
6 Oct 2026·5 min read
↗
From Input to Attack Chain: untrusted data reaches an interpreter, with a boundary check separating it from impact.
Web Application Security

From Input to Attack Chain

How input crosses trust boundaries—and how to reason about impact.
6 Oct 2026·6 min read
↗
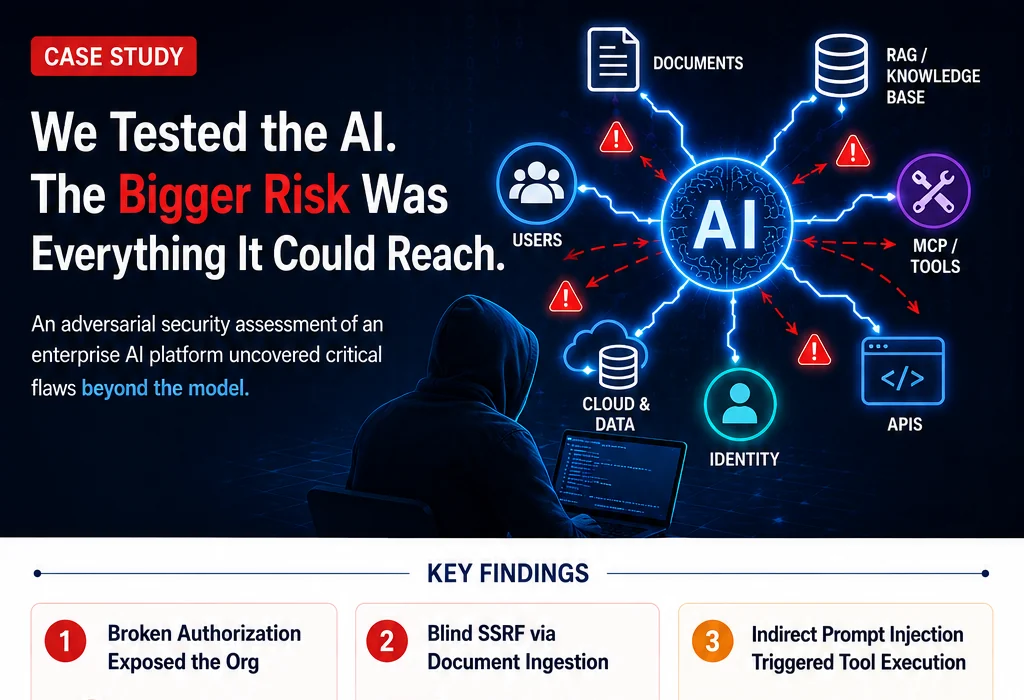
Illustrated summary of six attack paths identified during an authorized enterprise AI security assessment across users, documents, retrieval, MCP tools, APIs, cloud systems and identity.
AI Security

We Tested the AI. The Bigger Risk Was Everything It Could Reach.

Lessons from assessing the systems and tools connected to enterprise AI.
3 Sept 2026·7 min read
↗
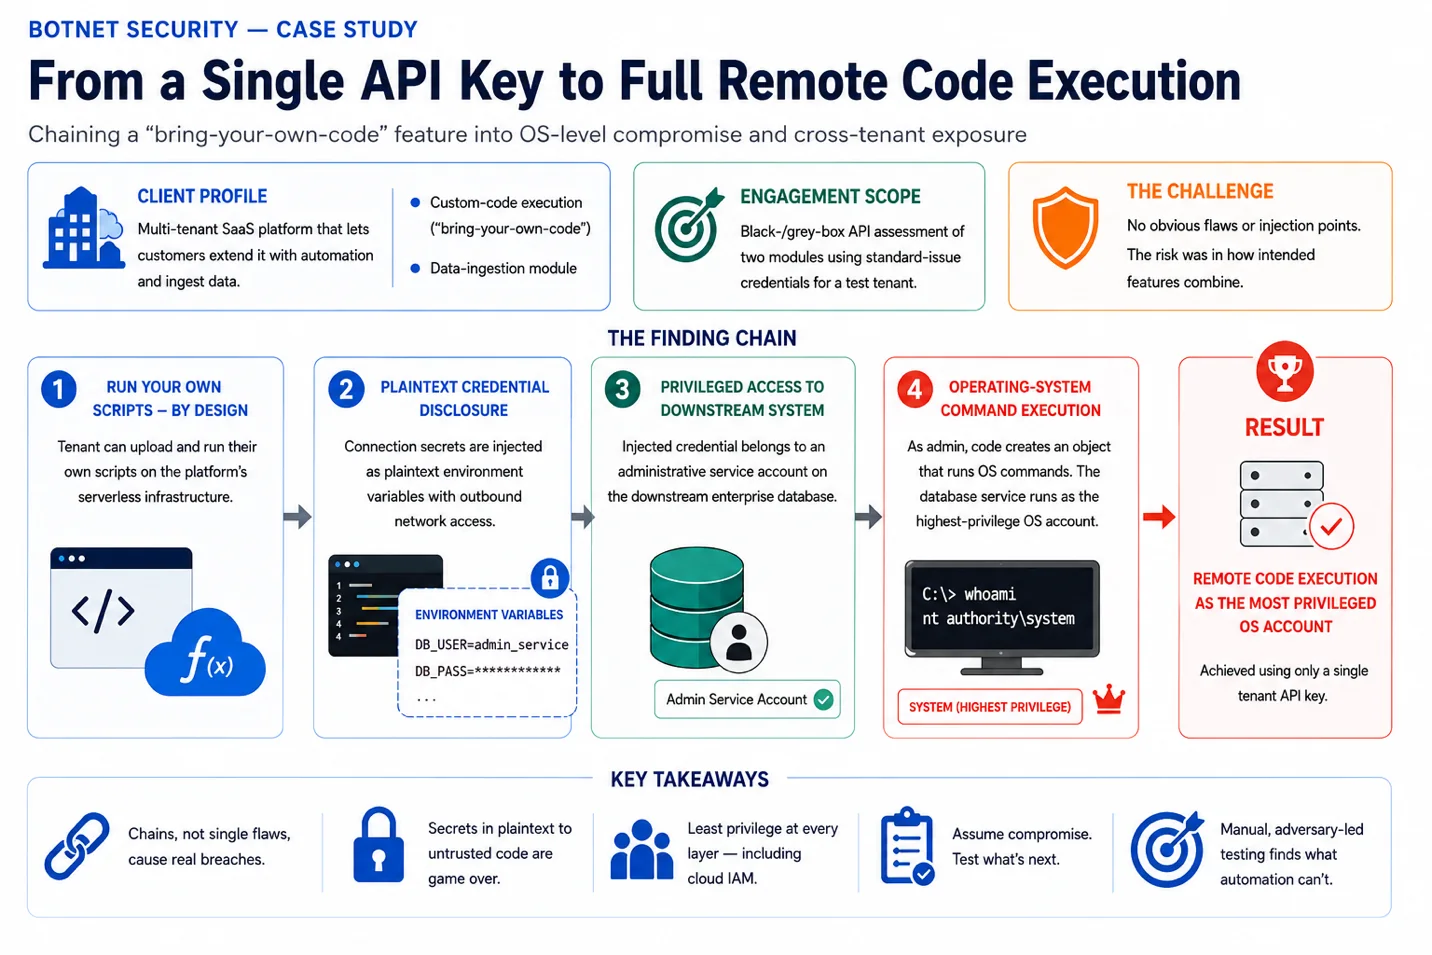
Attack-chain diagram showing how a tenant API key, customer-supplied code, exposed integration credentials and excessive downstream privilege combined into remote code execution.
API Security

When “By Design” Becomes a Breach

When intended API features combine with excessive privilege.
2 Sept 2026·7 min read
↗
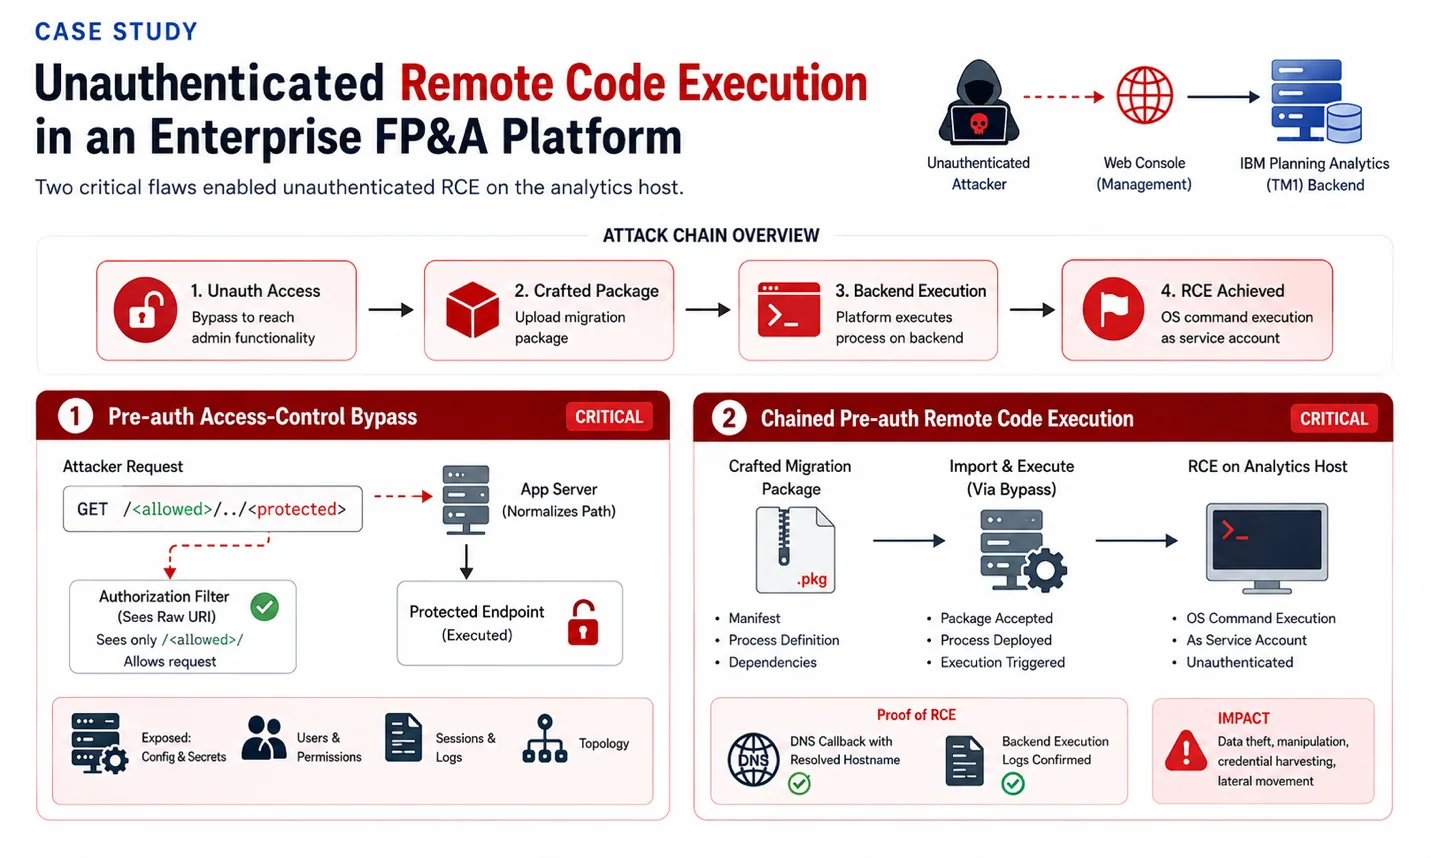
Attack-chain diagram showing a pre-authentication path-normalization bypass chained with a crafted migration package to reach command execution on an enterprise analytics host.
Web Application Security

Unauthenticated RCE in an Enterprise FP&A Platform

An enterprise case study in access-control and workflow failures.
2 Sept 2026·9 min read
↗
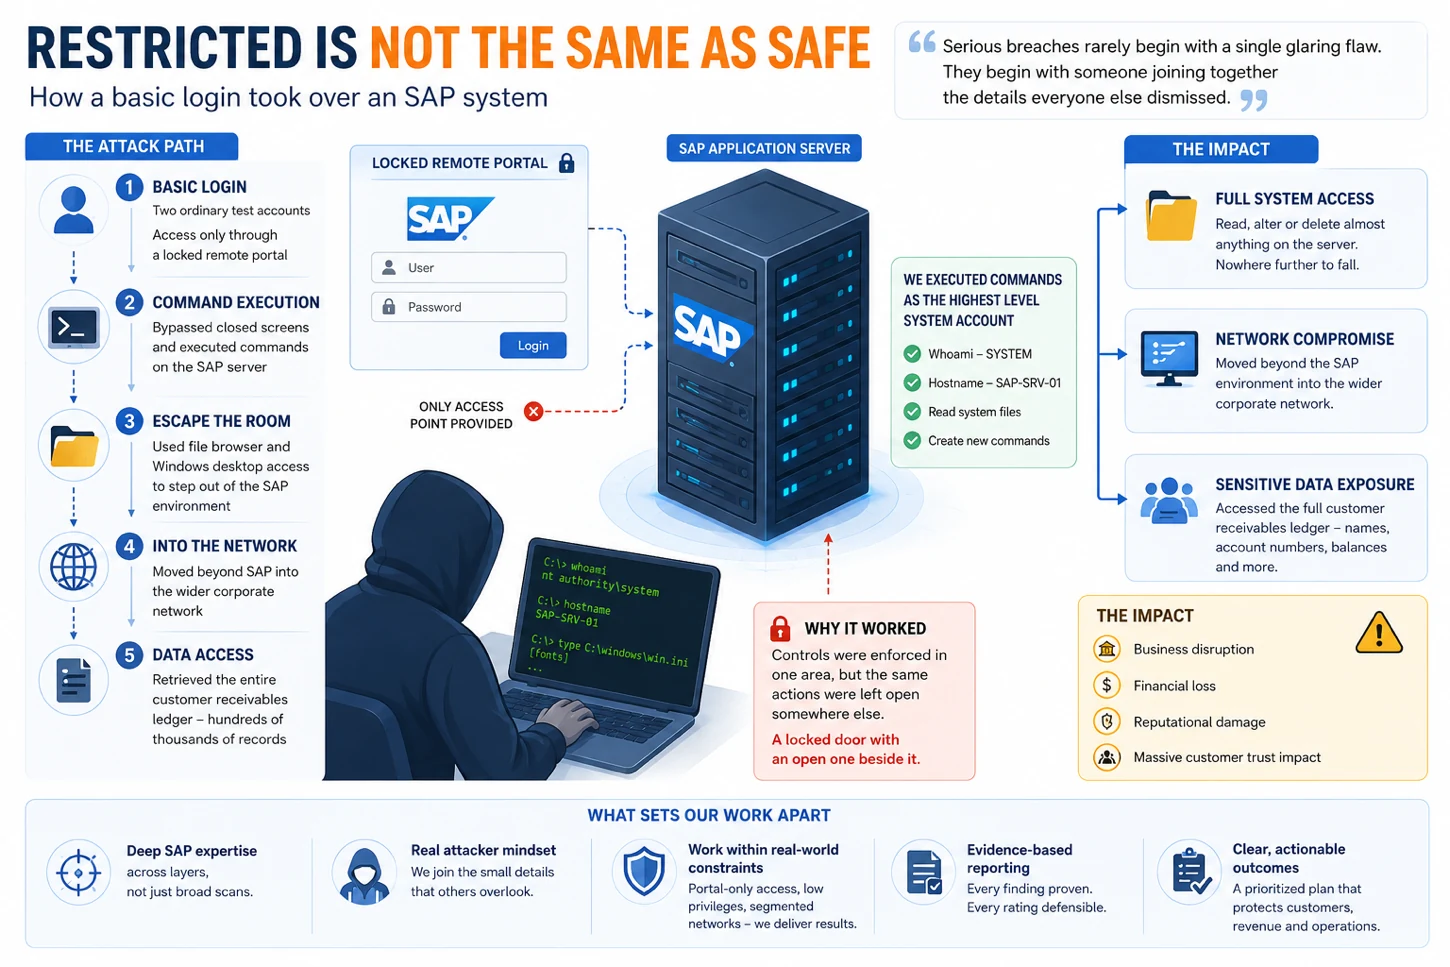
Diagram of an authorized SAP attack path from a basic login through command execution, network access and customer data exposure.
SAP Security

How a Basic Login Took Over an SAP System

What an authorized assessment revealed beyond the SAP login.

2 Sept 2026·7 min read
↗

Put these insights to work.

Discuss an assessment ↗
BOTNETSECURITY

Offensive security and autonomous continuous pentesting built around evidence that can be reproduced.

Request an assessment ↗
AssessWeb applicationsAPIsCloudInfrastructureSAPPenetration testing in India
AdversaryRed TeamPurple TeamSocial engineeringControl validation
ProductBotXpose overviewAutonomous AI pentestingHow it worksProof & evidenceAuthorization & safetyTesting coverageIntegrations
CompanyBlogPartnersCompanyContact
© 2026 Botnet Security
PrivacyTerms